AmbitiousProcess (they/them)

  • 2 Posts
  • 353 Comments
Joined 1 year ago
cake
Cake day: June 6th, 2025

help-circle
  • Using password login renders this vulnerability useless.

    This isn’t the case, though I can see how the article could lead you to believe that.

    It’s directly based on password rather than key input. The entire vulnerability is that typing a password longer than 256 characters automatically defaults to crypt() outputting the * character instead of a normal password hash, which is coincidentally the same default character used as the “hash” (not actually a value you could get from a normal hash, intended to be impossible to get from any normal password for that reason) for the built-in daemon account.

    When the Ars Technica article says “Second, the target system account must be configured to be passwordless”, what they mean is the default daemon account, which has a hash set to * by default, and thus wouldn’t normally be accessible via any hashed password… unless you happen to find out that the system chooses to not make a hash, and just send * if you type more than 256 characters.

    Look at https://sshhole.com/ if you want the details.


  • Better than iPad kids. Not ideal obviously, but still far better.

    iPads (and mobile devices/OS’s generally) are designed to be as simplistic and easily understood as possible. They abstract away complexity, have to make menus less cluttered and make buttons larger to accommodate how people use them, and the lower power processors also mean less functionality than desktop-based systems.

    If you grow up using less shit, you’ll learn how to use less shit.


  • Maybe try Ente then?

    Haven’t used it before myself, but I’ve heard good things, and it does have a memories feature, and it seems at least based on the examples on their website that it might generate something more than just “today x years ago”.

    Unsure to what degree it works though, and unfortunately Ente is also a paid service (though it is privacy focused, and I believe it has a FOSS app too)

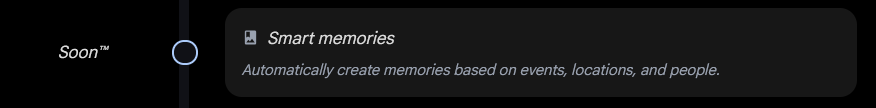
    Seems like “Smart Memories” are on the roadmap for Immich though, so you might just have to wait a bit and can then switch once they’re there:

    image

    There aren’t really any other mature options out there for self hosted, or even just private Google Photos alternatives in my experience, so you’re kinda just stuck with Immich for the most feature-complete replacement, and Ente for a more “just works” private but not self-hosted one. Everything else is basically just a glorified file browser, but maybe with some smart searching or better media codec support.


  • 100% Immich. Really good UI, and the kinds of quality of life features you don’t normally find in smaller open source apps (auto face tagging, map based on coordinates of photos, built-in non-destructive editor, memories, etc)

    The memories feature is mostly just “here’s photos/videos you took on this date”, but it doesn’t compile any sort of custom album based on a theme or place or anything like that. Not hard to do so yourself by just going to the map view and zooming into any location though.

    As for image searching it does have that, and I’ve found it to be shockingly reliable even when I run it on just a Raspberry Pi. (though it can take a while to give you the result of your search if you’re on lower-end hardware like that)


  • I would say if all you care about is having a nice looking, fully-featured, easy to use client, Proton is good, but if you really just need… an inbox with an email attached, then Tuta will be a little cheaper and just as private, just with less bells and whistles.

    If you care about removing yourself from other services like calendars, cloud storage, password managers, etc, Proton is way better since it has the full suite.

    For example, Proton supports auto-categorizing mail (e.g. newsletters, promotions, updates, transactions, etc), unlimited email aliases, a more modern UI, good integrations with Proton Drive and Proton Calendar if you decide to use those as well instead of Google Drive and Google Calendar, etc.

    Tuta is more just an inbox that you can bother to sort as needed, comes with some aliases if you feel like it but probably not enough for every single online service you have, has a basic calendar, but doesn’t have any kind of integrated Drive access (is still in closed beta rn), and has a more… basic UI.


  • The AI CEOs are experts at creating criti-hype.

    “Our product is so dangerous that you need us to keep you safe from it”

    “Our product is so capable it could outsmart every human being trying to stop it! Hey by the way, you want to replace your workers with our chatbot?”

    I don’t think a lot of these AI CEOs even believe it themselves. They just know that getting everyone to scream “It’s so powerful it could kill us all (without us in control)” is great for making business deals with companies that want a highly capable “thinking” machine, or pitching their infinite potential future growth to investors.


  • I mean… there’s hacker groups out there, and there’s people who are opposed to the livestream, so obviously there’s some groups that’d want to shut it off.

    The main issue is that the means of doing so are… pretty unlikely to exist or be possible to figure out how to exploit in time before it’s over.

    Realistically, they’d have to find a way to shut off all internet connectivity via every possible method to wherever it’s being streamed from, which is pretty unlikely. (would require someone to physically dig underground and cut off any copper/fiber optic lines, then also find a way to illegally and without being fox hunted use a signal jammer that blocks every single cellular signal, and also take down any satellite-based internet dishes)

    The alternative is if they can somehow, within the duration of the livestream, identify which device on all of the internet is streaming to whatever platform is hosting the stream (its IP wouldn’t be exposed to anyone other than the company hosting the stream), then also find vulnerabilities that would allow them into the device, or have the DDoS capacity to saturate the network that specific device is connected to (while also being able to do the same to every single possible backup device or network link that’s available)

    So no, realistically, probably not.